
Third-Party Cyber Risks: How to prepare insureds for digital supply chain cyber attacks
Here is a recap from our recent masterclass with FisherBroyles. The masterclass covered upstream and downstream third-party risks and how to mitigate those risks.
The Cyber Insurance Academy was thrilled to host Stuart Panensky from FisherBroyles for a recent masterclass discussing third-party cyber risks and ways to mitigate them. Stuart explained the cyber risks associated with third-party access to policyholder data, the best practices to mitigate those risks, how to identify risks in the policyholder’s upstream and downstream supply chain, and how to apply legal and regulatory requirements.
Business has become increasingly more connected over the years, with many companies heavily relying on third-party vendors for support. This widespread use of third parties increases access to policyholder data in both the upstream and downstream supply chains.
Read the rest with a free account
The library is open to anyone with an account — articles, white papers, market updates and the masterclass archive. It is free, there is no time limit, and nothing renews.
Already have one? Sign in
More from Guides
Does Insurance Cover AI? What Cyber and Liability Policies Say in 2026
No line of insurance fully covers AI yet, and most policies still say nothing about it. Here is our read of where AI risk sits in 2026.
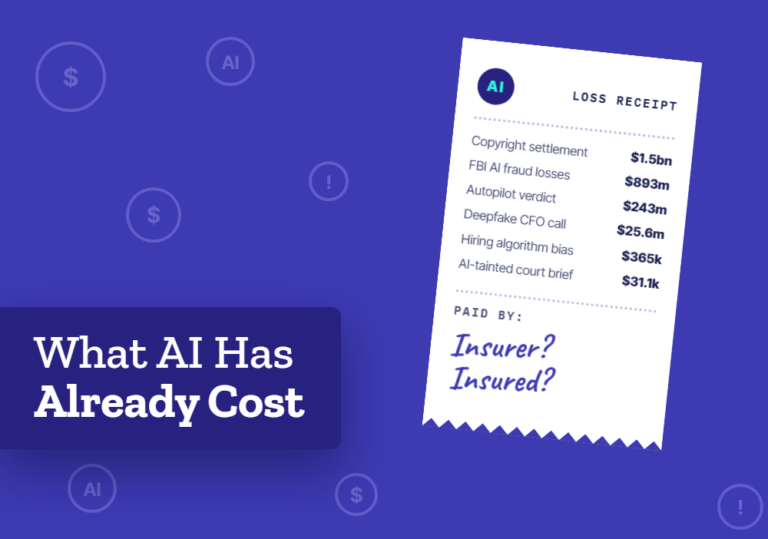
What Has AI Already Cost? AI Losses Through an Insurance Lens
AI losses already run from a $31,000 court sanction to a $1.5bn settlement. The harder question for insurers: who paid?
When Cyber Insurance Starts Dictating Ransomware Response
Cyber insurance is often described as a financial backstop - a way to transfer risk once the worst has already happened. In…